This guide to iGaming fraud prevention and payment risk management covers where fraud actually happens across the player lifecycle, which controls reduce it without cutting legitimate deposit approvals, and what to fix first on a limited budget. Short answer: a 2026 LexisNexis Risk Solutions survey of North American online gaming operators found that roughly 60% of fraud exposure occurs at account creation and withdrawal combined. Deposit-stage fraud remains material, while first-party and friendly-fraud disputes require a different defense from stolen-card fraud. The controls should therefore follow the stage and fraud type rather than concentrate only on deposits.
Everything below follows the shape of iGaming payment fraud itself: where it happens, what it looks like at each stage, how much protection costs in approval rate, what happens once a chargeback ratio climbs, and, the part most vendor content skips, what to actually build first.
The same survey found that 78% of respondents named bonus abuse as a top threat, which is why the next section starts there rather than with stolen-card fraud.
Short answer: nine fraud patterns account for most of what operators deal with, though most concentrate at a particular stage of the journey rather than splitting cleanly between them.
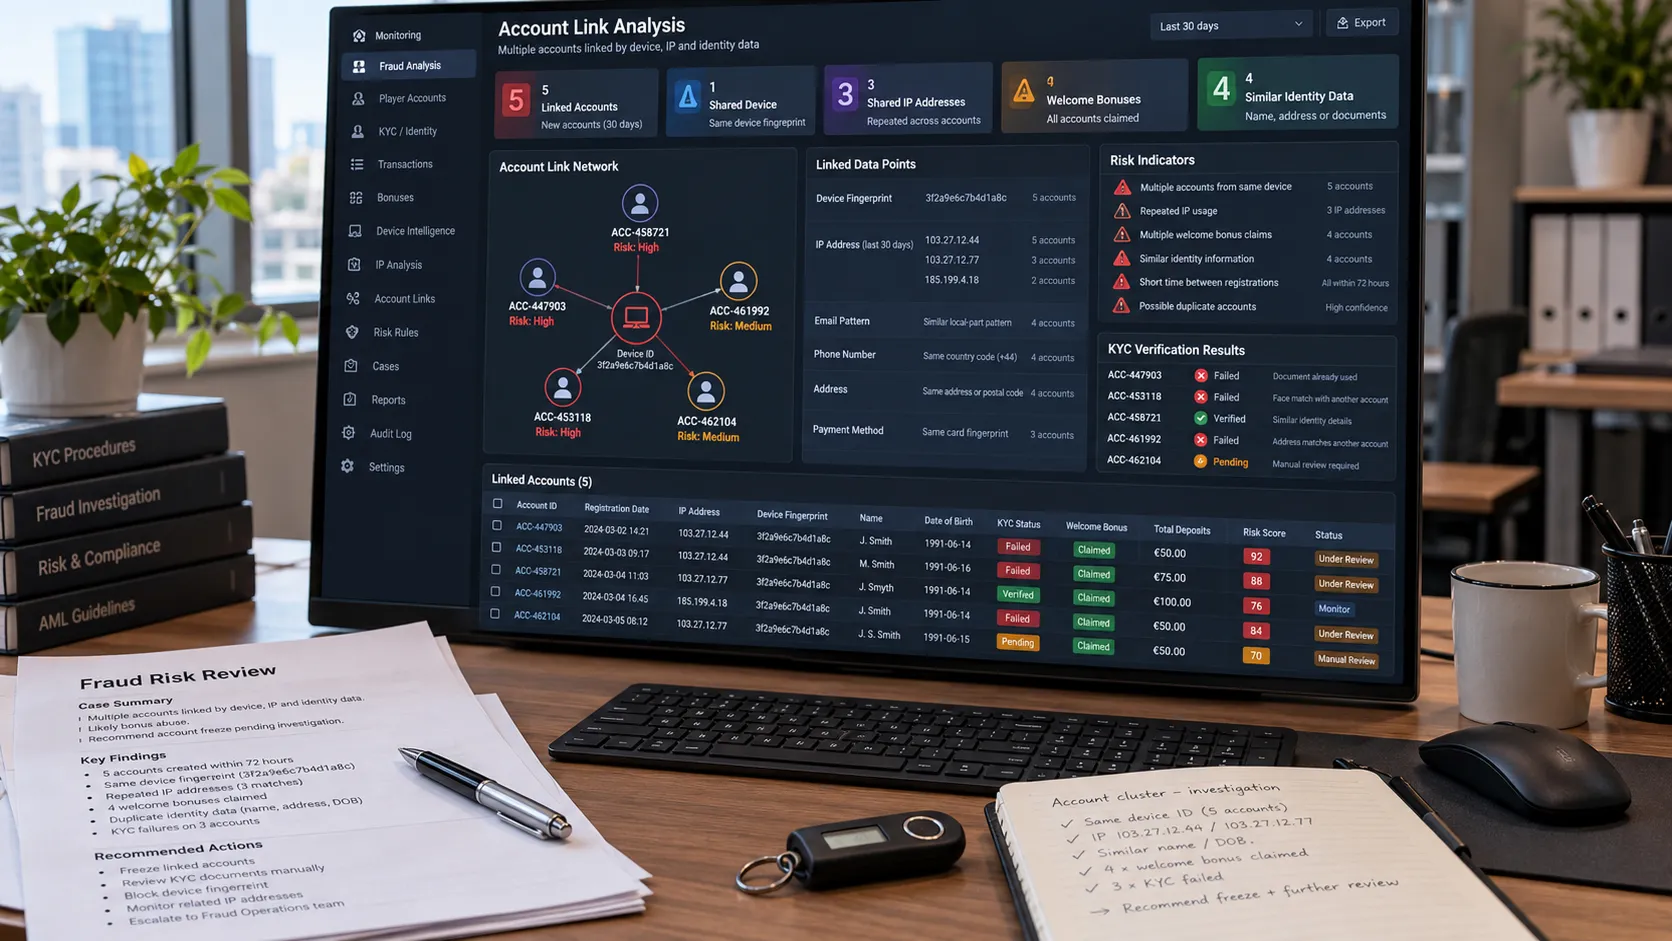
Bonus abuse is one of the most widespread fraud and abuse patterns in iGaming — the 2026 LexisNexis survey named it the top threat, cited above. LexisNexis also reported that one detected abuse network generated more than 95,000 fraud events and exposure of up to $3.2 million. The pattern often combines multiple accounts, synthetic or stolen identities, and repeated exploitation of promotional offers.
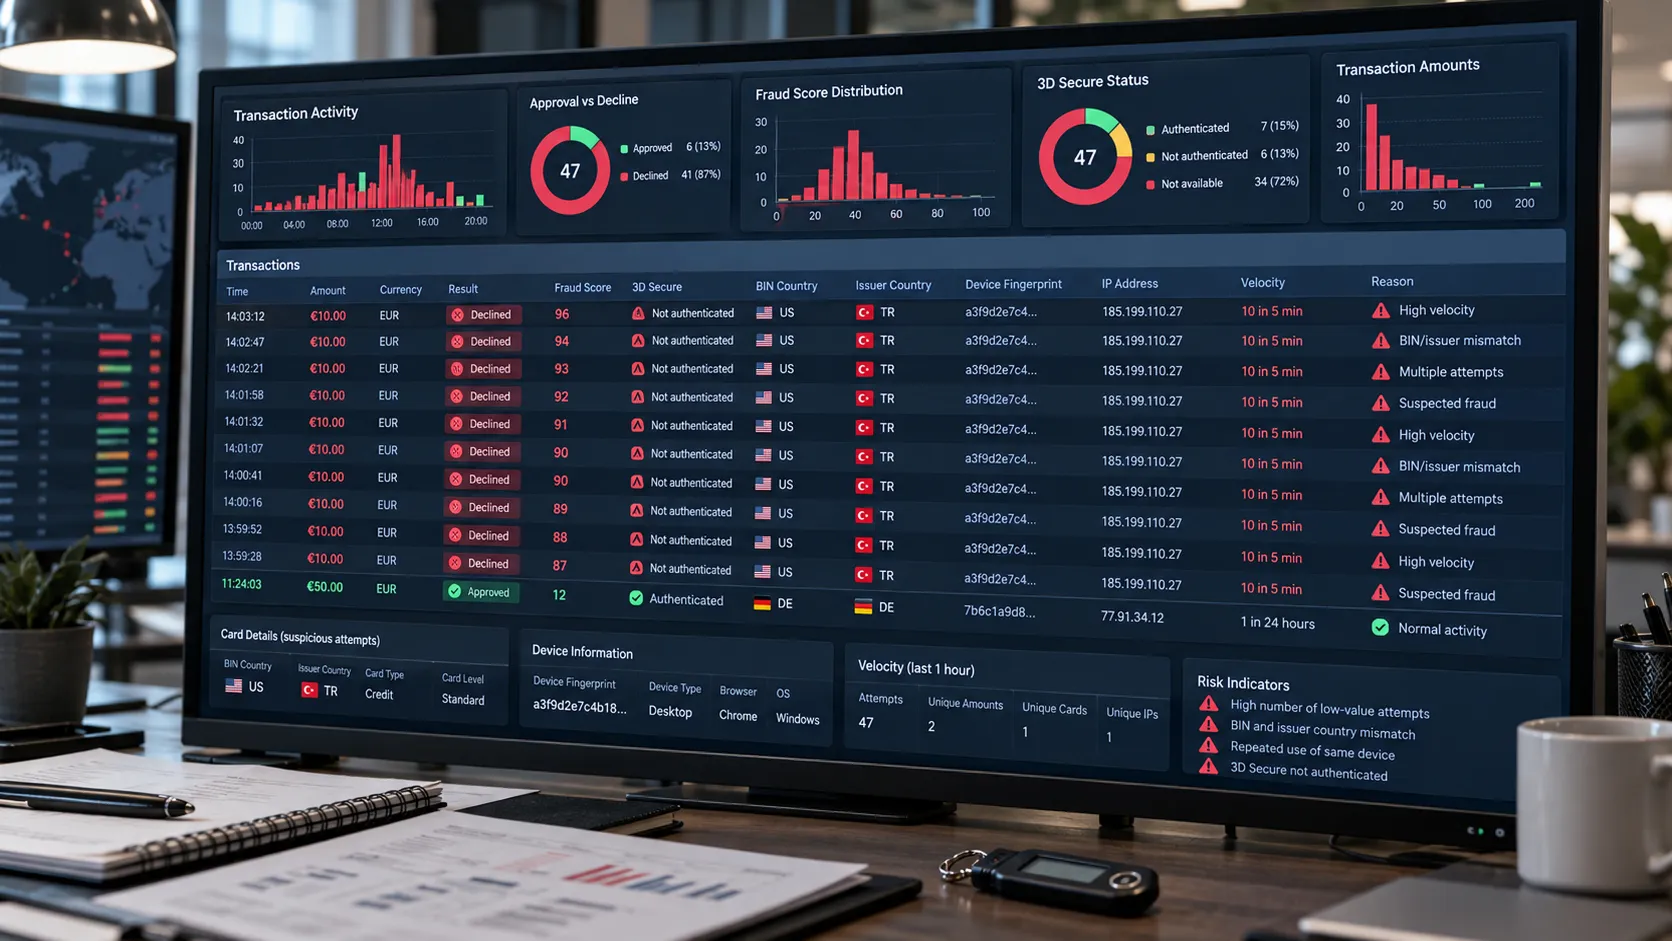
Fraudsters run small, rapid charges against stolen card numbers to find which ones still work before attempting a larger deposit. In iGaming, a successfully tested stolen card may later be used for deposits, bonus abuse or rapid cash-out attempts. For instance, a validated stolen card can fund a fresh account built purely to claim a welcome offer.
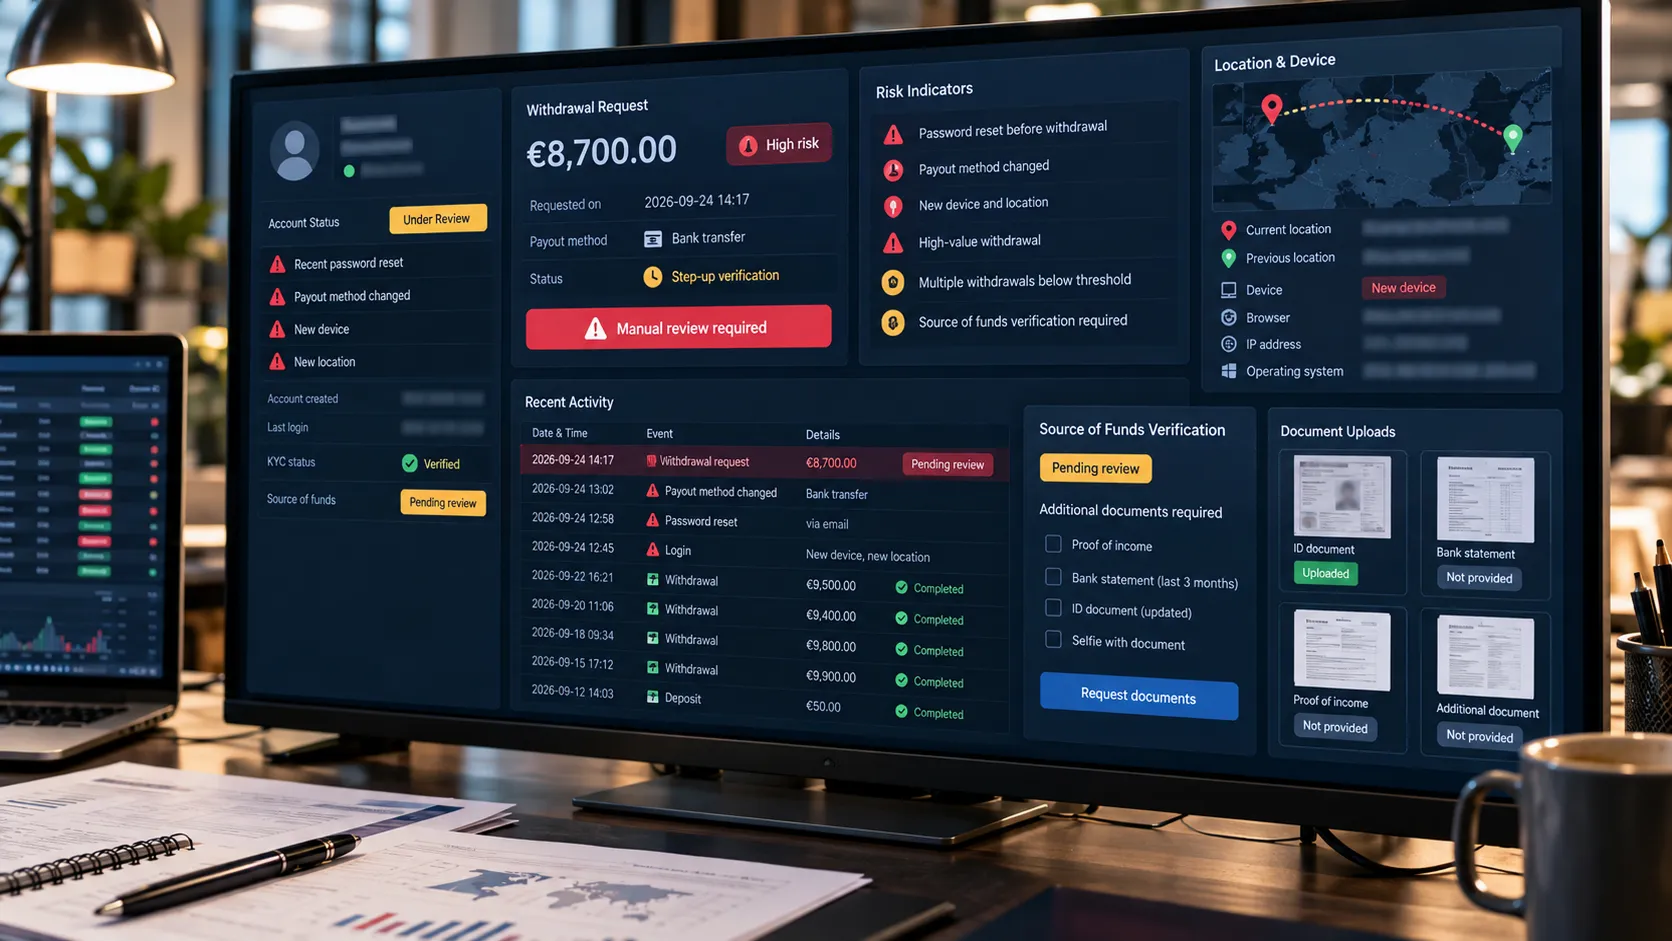
Account takeover occurs when an attacker gains control of a legitimate player’s account. Warning signs can include a new device or location, credential changes, unusual betting behavior, rapid balance movement, or an unexpected withdrawal request.
A synthetic identity blends real and fabricated data, a real national ID, tax ID, or address fragment combined with fabricated personal details, built to pass a shallow KYC check and then farm bonuses or launder funds through withdrawal. It surfaces earliest at registration, where email, phone, IP, and device signals either cohere into one plausible person or don’t.
Friendly fraud occurs when a cardholder disputes a legitimate transaction as unauthorized or otherwise invalid. In gambling, this can include intentional disputes after losses, but it can also arise from transaction confusion or unrecognized merchant descriptors. It’s covered in depth below because it needs an entirely different defense from the other fraud types on this list.
Automated bots operate across several fraud types at scale: automated account registration, credential-stuffing attacks using stolen login pairs, automated scraping of odds, pricing, or account data, rapid-fire testing of stolen cards, and exploitation of predictable bonus rules. Because bots run at machine speed and volume, a single unmanaged bot run can generate far more registration or bonus-claim attempts than a human fraud ring.
Collusion is a separate, human-coordination risk rather than an automation one: two or more players coordinate bets or gameplay to guarantee an outcome, often to launder funds or drain a bonus pool rather than to actually win. It shows up in gameplay and wagering patterns rather than in registration or payment data alone.
Gambling accounts offer a plausible reason to move money in and pull it back out, which is exactly why AML controls exist on the withdrawal side. Structuring, breaking a large transaction into several smaller ones to stay under a reporting threshold, is the specific pattern withdrawal-stage AML monitoring is built to catch.
Depositing through one payment method and withdrawing through another can create fraud and AML risk when verification standards differ or the operator cannot establish a consistent source and destination of funds. This is a payment-stack design problem as much as a fraud problem. The fix is aligning verification depth across every method, not just the ones seeing the most volume.
Short answer: operators often group bonus abuse, account takeover, stolen-card fraud, collusion, and money laundering under one broad fraud label. In practice, these risks can sit with different teams, use different metrics, and require different controls.
Game-integrity risks such as collusion rely heavily on behavioral and gameplay analytics. Payment fraud is measured through indicators such as fraud reports, disputes, and approval performance. Identity and account abuse rely more on KYC, device, and behavioral signals, while money laundering belongs to the AML compliance framework.
The table below maps each risk type to the metric it actually moves and the function that typically owns it.
A fraud filter stops a transaction before it happens. Friendly fraud happens *after* a completely legitimate transaction, when a player who lost money decides to dispute the charge rather than accept the loss. Pre-transaction fraud controls cannot prevent every later first-party dispute because the original payment may be legitimate. The defense therefore extends beyond transaction screening to clear merchant descriptors, purchase transparency, pre-dispute alerts, refunds where appropriate, and strong evidence for representment. Visa and Mastercard both offer post-purchase tools designed specifically to reduce unnecessary and first-party disputes.
Short answer: the right control depends entirely on which stage it’s protecting; a device fingerprint is worth little at withdrawal, and source-of-funds checks are generally risk-triggered rather than universal registration controls, though some operators may need them during onboarding under applicable regulatory requirements.
KYC verification and deduplication can help detect synthetic identities and repeat bonus abuse during account creation. Device fingerprinting and IP or geolocation signals can identify links between accounts that use different names or payment credentials.
Velocity rules flag unusual deposit frequency or amount jumps. BIN and issuer-country checks can flag inconsistencies between payment credentials and the player’s declared or observed location, though a mismatch is a risk signal rather than proof that the card is stolen. Geolocation and VPN detection catch a player masking their real location. 3-D Secure can shift liability for eligible fraud disputes when the transaction meets the relevant card-network, regional, and authentication requirements, but it is not a universal liability shift for every gambling transaction, and that distinction matters once a chargeback dispute reaches representment.
Payout limits and step-up verification slow down the fast cash-out pattern account takeover relies on. Source-of-funds checks and structuring detection, flagging several withdrawals just under a reporting threshold, are where AML and fraud controls overlap most directly, since both are ultimately asking the same question: does this money’s path make sense?
Short answer: every fraud control that blocks a bad transaction also risks blocking a good one, and in iGaming that tradeoff is measured directly in lost deposits, not just an abstract customer-experience metric. LexisNexis found that 81% of operators say even moderate onboarding friction is enough to drive a player to a competitor. Friction doesn’t just annoy a legitimate player; it loses the deposit and often the player entirely.
False positives create a measurable revenue cost, not just an abstract one, because legitimate players can abandon onboarding or deposits after an unnecessary decline or challenge. The right objective is therefore not the lowest possible fraud rate at any cost, but a control strategy that measures fraud loss and legitimate-player conversion together. Standalone fraud-detection tools are essential for risk scoring, but they usually do not control acquiring relationships, routing, or retry logic. A payment layer can improve authorization performance through routing and permitted retry logic after eligible soft declines, though hard declines or transactions rejected for fraud or compliance reasons should not simply be rerouted to bypass the original decision (more on this below).
Fraud controls and approval rate don’t have to trade off against each other one-for-one, but getting both right at the same time takes more than a filter sitting in front of the checkout. It takes a payment layer that supports eligible retries and routing alongside its fraud controls, not one working in isolation from them.
Short answer: these operate at different levels. A chargeback is a dispute over one specific transaction. Visa’s VAMP monitors the combined fraud-and-dispute ratio across a merchant’s transactions in aggregate, not any single chargeback. Restrictions or account termination are possible acquirer actions if that aggregate ratio stays above threshold, not an automatic next step after one dispute. The window to influence that ratio starts earlier, and is narrower, than most operators assume.
Fill out the form, and we will contact you
Card networks monitor dispute-to-transaction ratios directly. Visa’s Acquirer Monitoring Program (VAMP) measures card-not-present fraud and disputes with a combined count-based ratio rather than a traditional chargeback ratio. From 1 April 2026, the Excessive Merchant threshold in Asia Pacific, Canada, the EU, and the U.S. is 150 basis points (1.5%), with at least 1,500 monthly fraud and dispute events. For card-not-present VisaNet transactions, the ratio is calculated as fraud reports (TC40) plus disputes (TC15), divided by settled transactions (TC05) (Visa).
Exceeding a VAMP threshold can trigger remediation and additional acquirer oversight. Commercial chargeback fees, reserves, and account actions depend on the acquirer and merchant agreement. Visa’s public VAMP fact sheet does not state one universal per-transaction merchant fee.
Ethoca and Verifi enable participating merchants and issuers to exchange fraud and dispute data, often through payment providers or integration partners, surfacing a dispute the moment a cardholder contacts their bank, often days before it would otherwise become a formal chargeback. Depending on the program and timing, a merchant may be able to resolve an inquiry or dispute before it progresses further. Visa’s VAMP methodology excludes certain disputes resolved through eligible pre-dispute solutions, subject to the timing of the data extract.
Representment wins on documentation, not on argument, but requirements depend on the card network, dispute reason, region, and transaction. A strong evidence file can include the following where relevant:
Automation can reduce the manual work required to collect transaction, account, authentication, and gameplay evidence before the applicable network deadline.
Short answer: compliance and fraud prevention overlap heavily but answer different questions: fraud controls ask “is this really the account owner,” compliance asks “is this money and this player’s activity legal to process.”
A working AML/KYC program typically runs in four stages. Customer due diligence at onboarding verifies identity and assigns a risk level based on transaction patterns and jurisdiction. Enhanced due diligence applies to higher-risk players, politically exposed persons, or unusual deposit patterns, and adds source-of-funds and source-of-wealth checks on top of standard verification.
Self-exclusion controls are stronger when payment rails help enforce them. A player who self-excludes on one platform but reopens deposits through a different account or method breaks the entire control. Primary responsibility for enforcing self-exclusion sits with the operator, its player-identification systems, and its responsible-gambling tools; payment data can only serve as an additional signal for that control, not a substitute for it.
Crypto payments introduce additional AML considerations because operators may need to assess wallet and transaction risk alongside conventional KYC and source-of-funds controls. Blockchain-analytics tools can help identify exposure to sanctioned addresses, mixers, illicit services, or other risk indicators. The exact screening, source-of-funds, and monitoring requirements depend on the operator’s jurisdiction, license, custody model, and payment-provider structure.
Licensing requirements shift by market, but so does what a license actually requires on the payment side. Some regulators mandate specific source-of-funds thresholds, cooling-off enforcement, or deposit-limit tooling as a condition of the license itself, not just as good practice. A compliance program built for one jurisdiction’s requirements rarely transfers cleanly to the next without a specific review.
Short answer: fraud, chargebacks, compliance, and finance can sit under different leaders and use separate systems. When risk signals are not shared between those functions, an operator can miss patterns that are visible only across account, payment, and dispute data.
When a fraud team flags a pattern the chargeback team never sees, or a compliance officer only learns about a dispute spike from a regulator’s inquiry, the failure isn’t any one team’s judgment. It’s the absence of a shared picture. A single owner or a shared risk dashboard across these functions closes that gap directly, and it’s worth doing even without a reorganization: one dashboard that tracks chargeback ratio, approval rate, and flagged-account volume together can surface patterns none of the underlying teams would catch working from separate reports.
The same silo problem shows up between operators, not just within them. LexisNexis found that only one in five North American gaming operators in its 2026 survey currently shares fraud intelligence with peers or industry networks. This means the same abuse ring, device fingerprints, and stolen card batches can get rediscovered independently by each operator it targets, one at a time, instead of being flagged once and blocked everywhere.
Short answer: for most operators, registration-stage identity checks and chargeback-ratio visibility are the highest-impact starting point, though exact cost and priority depend on fraud profile, transaction volume, market, and existing infrastructure. Everything else in this guide builds on getting them right.
The following sequence is an illustrative prioritization framework rather than an industry-standard implementation timeline; actual cost and priority depend on fraud profile, transaction volume, market, and existing infrastructure.
Short answer: these aren’t competing options so much as different layers of the same stack, and most mature operators end up running more than one at once.
A standalone fraud-detection tool primarily scores or challenges risk, and it can be very effective for that specific job. Unless it is integrated with payment orchestration, though, it may not control acquirer selection, payment routing, or retry logic. A payment provider can operate at a different layer, using fraud signals together with routing rules and acquirer performance data. The two functions can complement each other rather than replace one another.
BillBlend states that its platform combines real-time fraud monitoring, chargeback-management tools, payment routing, 3-D Secure support, and onboarding controls. The company also states that its infrastructure supports 100+ payment methods and 70+ currencies.
Treating fraud, chargebacks, and compliance as one connected system, rather than three separate scorecards, tends to close more gaps than tightening any single filter alone.